For educational and research purposes only - only test systems you own or have explicit permission to test.
The Goal
I want to clone a MIFARE Classic 1K card with my Flipper Zero. 24 of 32 keys unknown, no reader access. Card-only attack because I don’t want to go to the card reader to test ;-)
The Rabbit Hole
The tooling landscape is a graveyard:
- FlipperNested - EOL since 2023
- HardnestedRecovery (PC) - silently skips every log line containing dist, which current firmware writes on all of them
- FlipperNestedRecovery (PC) - old log format, crashes on heap corruption
- MFKey FAP (on-device) - works, but slow and memory-hungry
Since most custom flipper firmwares integrated nested attacks into the NFC app, there’s simply no working PC tool for the new log format. The community went on-device and never ported back. But the flipper device is slow when you need a CPU find all the potential keys.
The Missing Piece
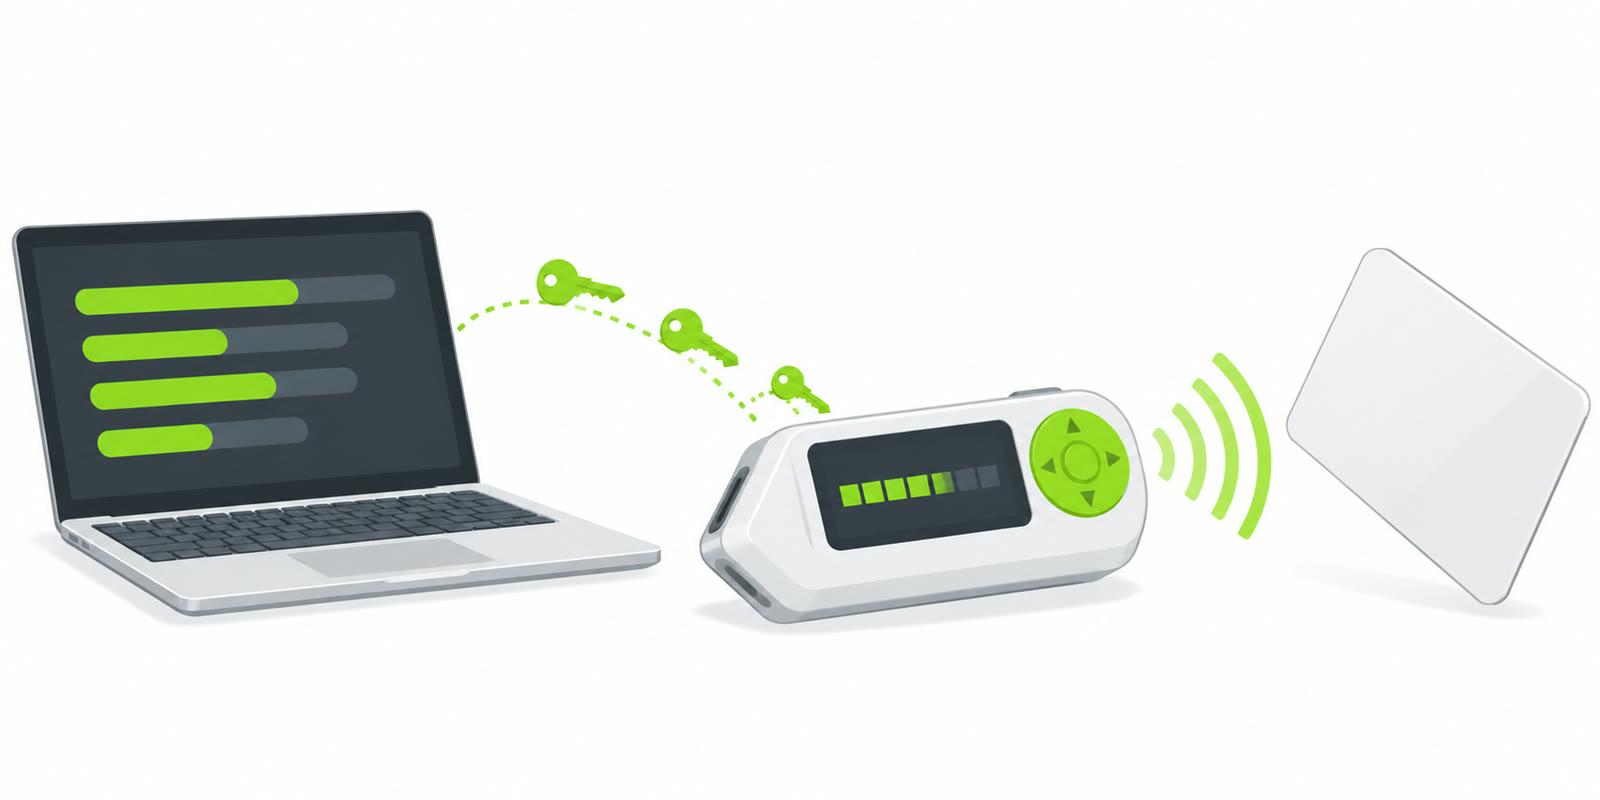
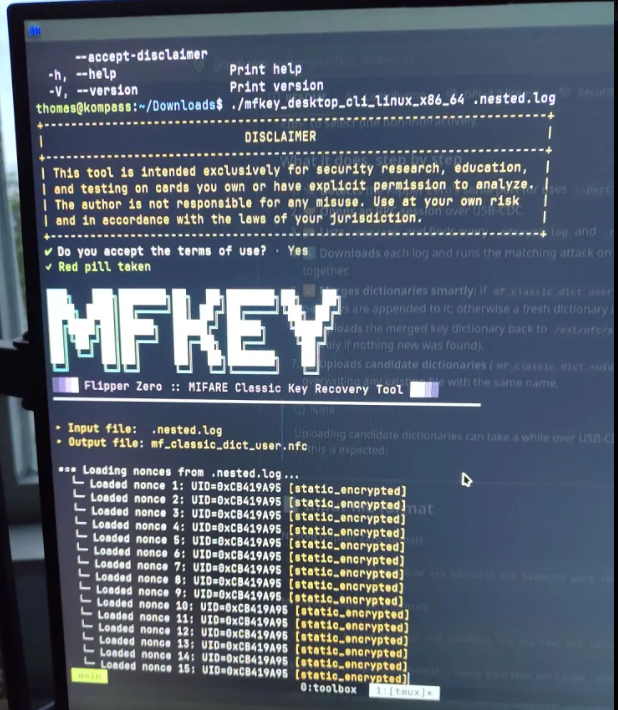
mfkey_desktop_cli - multithreaded desktop recovery: pulls .nested.log from the Flipper, cracks on all CPU cores, uploads candidate dictionaries back. Laptop does the math and the power, Flipper does the radio to find out the correct keys.
The Catch
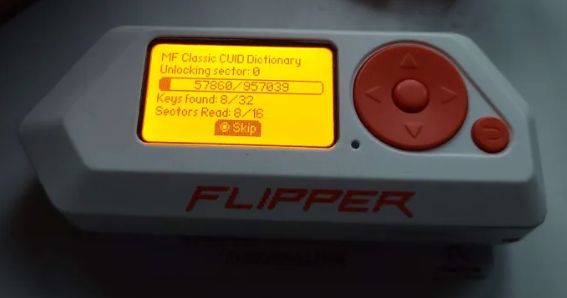
My card has static encrypted nonces - every auth returns the same nonce. Instead of one key per sector: 957,039 candidates. The Flipper then verifies them against the card at ~60 keys/sec. Full run takes days; trimmed to the sectors you need: about an hour.
Three Takeaways
1. Check the nonces first: identical nt0 = static card = candidate explosion
2. Reader access beats everything - one tap gives mfkey32-grade nonces and usually a single key
3. The desktop tooling gap is real - the solver cores are open source, someone just needs to connect them
But if you try and error hard enough you always win :)
Happy hacking!